+6.11%
+7.03%
+2.52%
+5.94%
+9.78%
+6.62%
How We Got Here
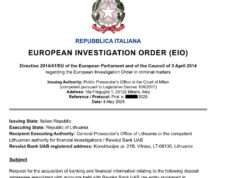
Revolut first confirmed handing customer data to an attacker impersonating a government agency after a group calling itself iamnotavillain spent months emailing the company using an authentic Italian government domain. The emails passed standard authentication checks because they genuinely originated from a real government mailbox, not a spoofed one.
As we reported, that mailbox was compromised through commodity infostealer malware on a government employee’s device in the Reggio Calabria prefecture, not a novel breach of state infrastructure. Revolut’s compliance team acted on the requests because they carried the legal weight of Italy’s certified PEC email system, which functions like registered post and passed SPF, DKIM, and DMARC authentication.
The group later escalated its claims, alleging it had also compromised broader Italian law enforcement systems and exfiltrated 147GB of internal police data. As we covered at the time, those claims remain sourced only to the attacker and a single intermediary X account, with Italy’s Interior Ministry never confirming a systems breach beyond the one mailbox.
The Ransom Demand
Revolut confirmed the customer data disclosure on September 12 and notified affected customers the same day. The attackers then published a demand for 6,000 Monero (CRYPTO:XMR) on September 16, valued at roughly $3 million, with a 24 hour deadline attached.
Revolut states it has received no direct ransom demand itself. That leaves 680 confirmed individuals, primarily high-net-worth crypto holders concentrated in Switzerland and France, in limbo while a public demand circulates without any formal channel back to the company that was breached.
An earlier, far larger demand for 10,000 Bitcoin, roughly $780 million, circulated under the name Revolut Smilik. Iamnotavillain claims this figure came from an impersonator entirely unconnected to their operation, which lines up with the turf war we detailed previously between the original group and a rival claimant fighting over ownership of the stolen data. Only the underlying data disclosure is confirmed. The ransom figures themselves should be read with that dispute in mind.
Why Monero Instead of Bitcoin
The choice of Monero over Bitcoin is deliberate. Bitcoin transactions are publicly recorded and traceable, which lets blockchain analysis firms monitor payments and blacklist wallets connected to criminal activity. Monero’s protocol conceals sender, receiver, and transaction amount, generating unique temporary addresses for each transfer, which makes it a common choice for extortion payments that need to stay untraceable.
This same traceability gap is what enabled the original targeting. Attackers reportedly used blockchain analysis to identify Revolut accounts tied to significant cryptocurrency holdings, then submitted fraudulent requests naming those specific wallet addresses. Anyone whose Bitcoin holdings are traceable to a Revolut-linked deposit could be identified this way, regardless of how carefully that person otherwise protects their identity.
What the Stolen Data Can and Cannot Do
Revolut has verified that the released data does not include cryptographic private keys, account passwords, or full payment card details. Passport scans alone cannot facilitate cryptocurrency transactions.
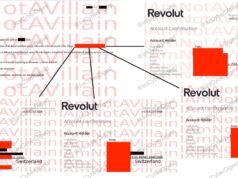
The stolen files still contain passports, verification selfies, addresses, IBANs, and complete transaction histories including cryptocurrency activity. That combination is enough to pass identity checks at other financial institutions, and it reveals which platforms a person uses along with their approximate crypto holdings. Blackmail attempts using these documents are already targeting individuals in the cryptocurrency industry, with customers who ignored earlier notifications now receiving direct extortion messages, particularly those relying on weaker authentication methods.
The Regulatory Problem Nobody Has Fixed
Revolut has notified law enforcement, blocked the fraudulent email channel, and maintains that core systems and customer funds remain untouched. UK regulators are reviewing the situation, which arrives shortly after Revolut secured conditional approval to operate as a national bank.
The mechanism behind this breach exposes something broader than a single incident. EU anti-money-laundering law requires regulated entities to respond to authenticated state requests, but provides no way to verify that the state behind an authenticated request is actually who it claims to be. Refusing carries fines running into the millions. Verifying is, under current rules, functionally impossible. Every bank or exchange handling law enforcement requests across FATF-obligated jurisdictions carries this same exposure, which means the 680 affected Revolut customers are not dealing with a Revolut-specific failure so much as a structural gap that any similarly positioned institution could fall into next.
Follow Hashlytics on Bluesky, Facebook, LinkedIn , Telegram and X to Get Instant Updates