+0.02%
+0.10%
+3.93%
+0.48%
+0.39%
+3.05%
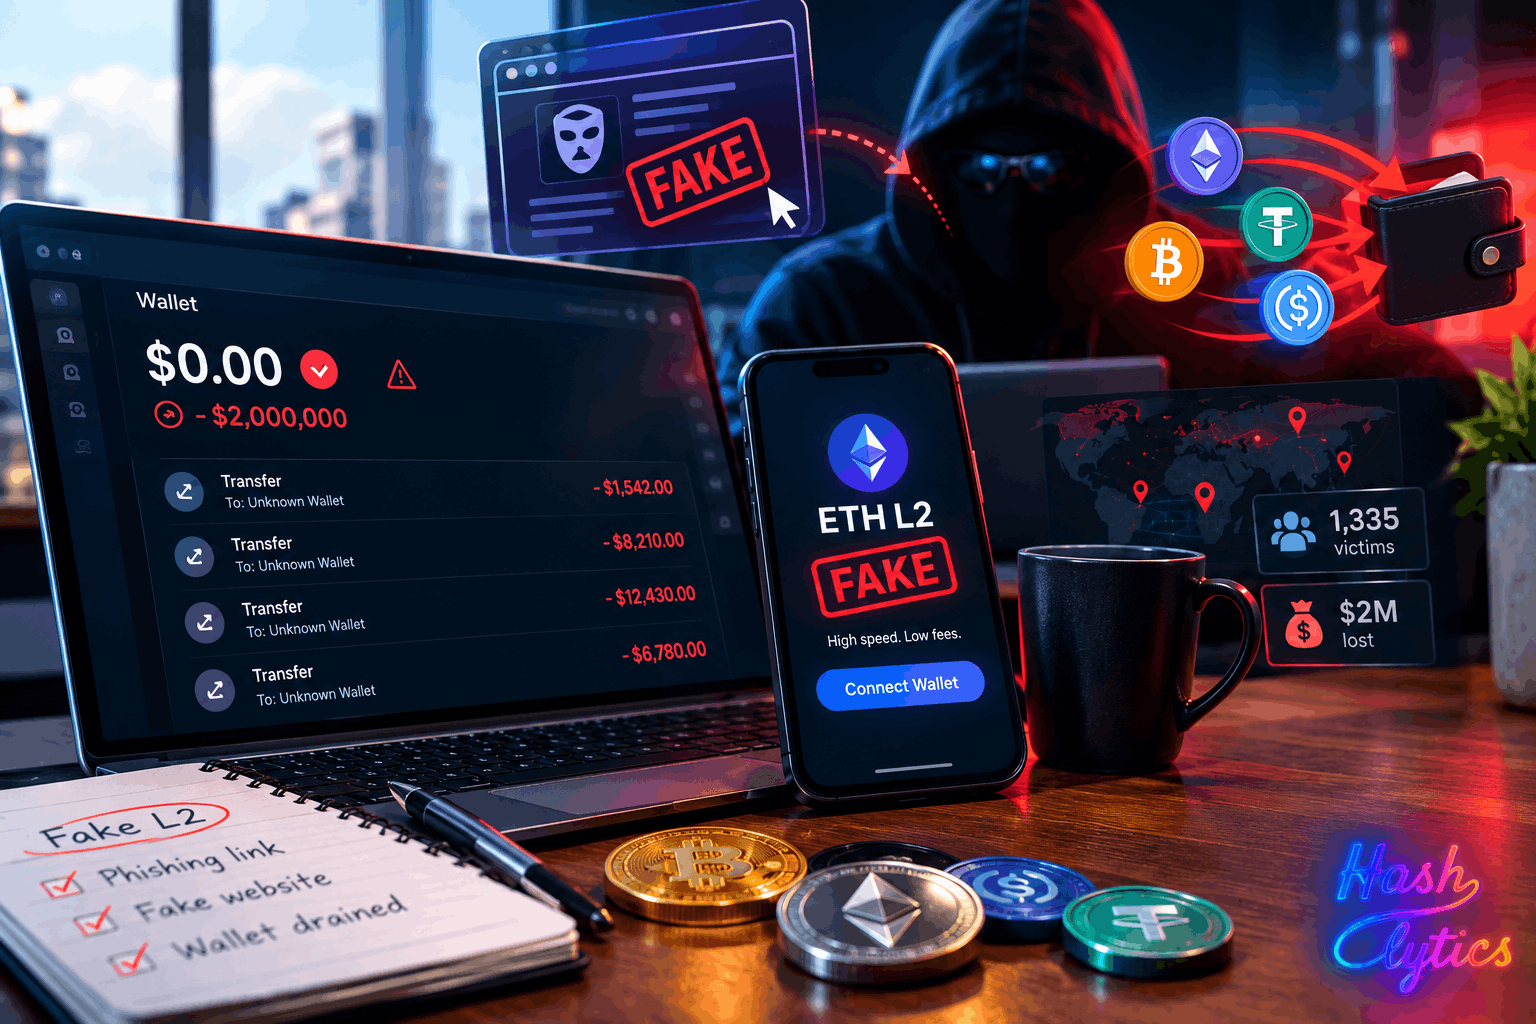
An unidentified group of scammers launched a fraudulent L2 chain masquerading as the Giwa mainnet, stealing approximately 766.25 ETH, valued at over $2 million, from unsuspecting users. The fake chain used 9134 as its Chain ID.
How the Fake Chain Fooled Everyone
DYORSWAP, a multi-chain decentralized exchange (DEX), initially identified the chain as legitimate. That listing led early adopters to bridge funds, hoping to get in early on what looked like a real launch. The actual Giwa project has confirmed it has not yet launched its mainnet.
This wasn’t a simple address impersonation. According to DYORSWAP’s official report, the fake chain deployed an OP stack style infrastructure complete with a functional bridge and a batcher, the kind of technical setup that takes real planning, not a quick copy-paste job.
Transactions, including buys, sells, and token launches, ran in real time on the fake chain. That activity gave the deception further credibility, and over 1,335 addresses bridged funds before the theft was executed.
DYORSWAP’s Response and the Backlash
After detecting the fund drain, DYORSWAP issued a warning telling users to avoid any unofficial Giwa mainnet RPC, bridge, or contract. The real Giwa project clarified on social media that its mainnet was never running.
DYORSWAP denied direct responsibility, stating the funds were drained from the fake chain itself rather than from any DYORSWAP infrastructure. They did initiate a reimbursement process, distributing over 200 ETH from their own reserves. Users pushed back anyway, arguing that DYORSWAP’s initial listing was what made the scam credible in the first place.
Part of a Bigger Pattern
This fake L2 scheme follows a string of high-profile security incidents across crypto. Both decentralized and centralized platforms remain active targets. Recent events include the Bitget breach, where hackers drained about $350 million across seven blockchains.
DYORSWAP says it continues to investigate the incident, aiming to reconstruct the fake chain’s transaction history to trace the attacker’s addresses.
Hashlytics Take
- DYORSWAP calling this “not our responsibility” doesn’t hold up well. Listing a chain is an implicit endorsement in DeFi, and that listing is exactly what turned a scam into a $2 million one.
- The reimbursement covers roughly a tenth of the losses. Framing that as a resolution understates how much of this falls back on users who trusted a platform’s due diligence.
- The real story here isn’t the scam’s sophistication. It’s that a decentralized exchange still functions as a trust signal, and that trust has no accountability structure behind it when it fails.
Follow Hashlytics on Bluesky, Facebook, LinkedIn , Telegram and X to Get Instant Updates