+1.19%
+1.19%
+5.99%
+1.43%
+5.14%
-0.67%
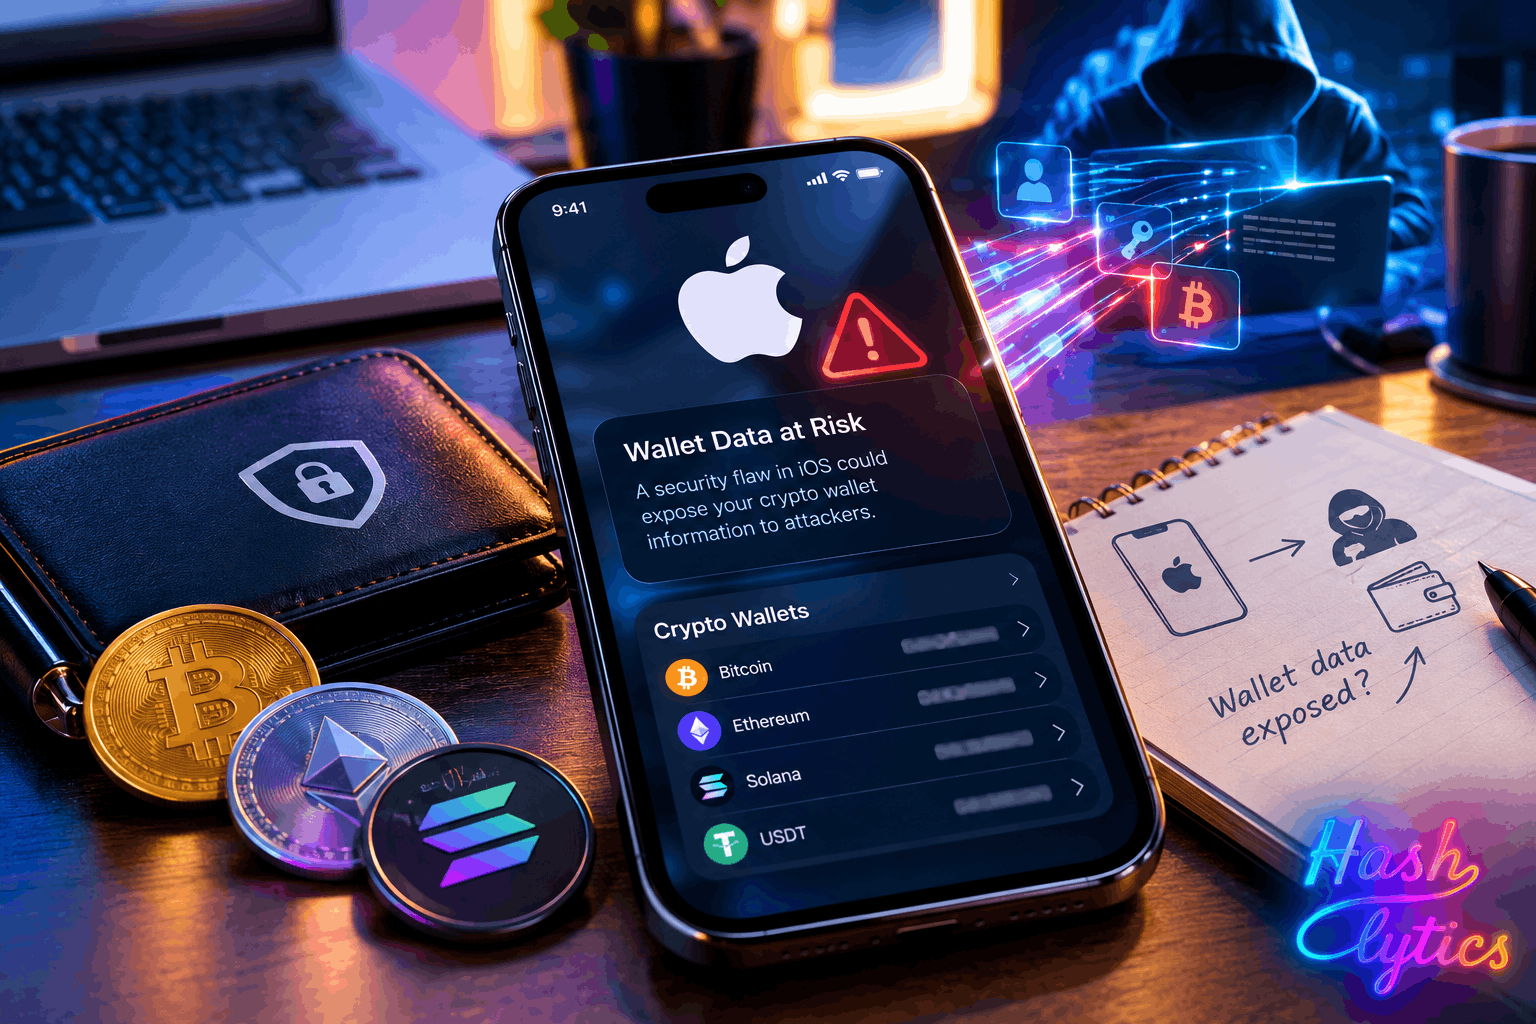
The attack starts with a social engineering trick. Victims are lured into opening a malicious page in Safari, which then exploits a flaw inside WebKit and JavaScriptCore to gain unauthorized access to critical user data. From there, attackers can extract information directly from the iOS keychain and any installed crypto wallet apps on the device.
How the WebKit Exploit Actually Works
The exploit leverages memory corruption inside WebKit, which lets attackers bypass built in security protections and escape the app sandbox entirely. In the worst cases, it can achieve kernel level root access, meaning near total control over the device.
SlowMist Chief Information Security Officer 23pds detailed the mechanism behind the attack. Once the initial JavaScript layer is compromised, attackers gain native call capabilities, which grants them arbitrary read and write access across the system.
iPhone versions from iOS 13 through iOS 26.5 may be affected, a broad range that highlights how widespread the potential risk could be, though the full extent has not been officially confirmed. Some reports indicate attackers have adapted an existing exploit known as Darksword
, which previously targeted older iOS versions and now appears to work against iOS 26.5 as well.
- Update your iPhone to the latest iOS version immediately
- Avoid opening untrusted or unfamiliar links inside Safari
- Exercise extreme caution if you store wallet keys or recovery phrases anywhere on your phone
- Consider moving sensitive crypto assets to a hardware wallet instead
Regular iOS security updates remain one of the simplest and most effective defenses against this kind of threat.
The vulnerability adds to a growing list of persistent cybersecurity risks facing cryptocurrency holders, and reinforces a familiar concern in the space: storing sensitive recovery information on an internet connected device carries risk no matter how careful the user is. Digital asset holders in particular remain frequent targets precisely because a single successful exploit can drain a wallet completely. SlowMist issued the original warning, and the full implications of the exploit are still being confirmed.
Hashlytics Take
The iOS 13 to 26.5 range is doing a lot of work in this story without much backing it up. That’s not a confirmed vulnerability window, it’s SlowMist’s estimate of what could theoretically be exposed based on the exploit’s mechanics, and there’s a real difference between those two things. What’s actually verifiable here is narrower: a WebKit flaw exists, a known exploit has apparently been adapted to reach it, and keychain data is the target. Until Apple confirms scope and ships a patch, the sensible move isn’t panicking about every iOS version since 2019. It’s getting off iOS 26.5 the moment a fix lands and treating any phone that stores a recovery phrase as a liability regardless of which exploit is making headlines this week.
Follow Hashlytics on Bluesky, Facebook, LinkedIn , Telegram and X to Get Instant Updates