

Lazarus Group Linked to Bybit Hack, Coinbase Faces $400M Costs
North Korea's state-sponsored Lazarus Group has been linked to a series of significant cyberattacks across the cryptocurrency landscape, including a February 21, 2025, exploit...

Microsoft CEO Admits Copilot Integrations Don’t Work
Microsoft's CEO Satya Nadella has internally criticized the company's own AI assistant, stating that key integrations for Copilot don't really work and are not...

Flow Blockchain Rollback Sparks Validator Halt Request
The Flow blockchain network performed a chain rollback to reverse a $3.9 million theft, prompting a key partner to call for a complete halt...

Trust Wallet breach drains $7M from Chrome extension users
Trust Wallet experienced a security incident affecting its Chrome browser extension, specifically version 2.68, resulting in approximately $7 million in unauthorized cryptocurrency being drained...
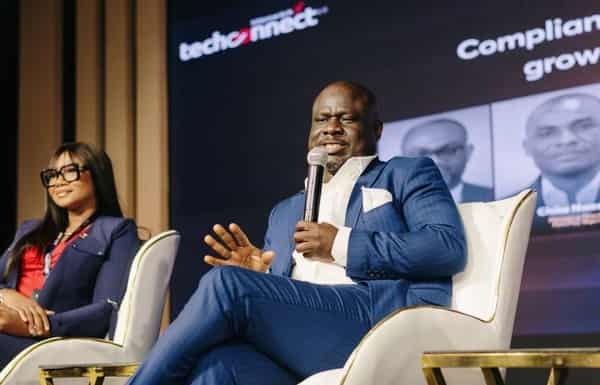
Nigeria’s Banking Trust Hinges on Cybersecurity & Regulation
Union Bank of Nigeria's Chief Information and Technology Officer (CITO), Wale Williams, recently highlighted the critical role of cybersecurity, regulatory compliance, and innovation in...

Coinbase Ex-Agent Arrested in India for Exchange Hack
A recent arrest in India has brought new clarity to a major security breach involving cryptocurrency exchange Coinbase, underscoring persistent risks tied to insider...

Spain’s 2026 MiCA & DAC8 Laws End Crypto Anonymity
The raw intelligence provided for this report focuses exclusively on Spain's upcoming implementation of the Markets in Crypto Assets (MiCA) and DAC8 regulations, set...

TRM Traces Stolen Crypto from 2022 LastPass Breach
TRM, a blockchain intelligence firm, announced that it has traced over $35 million in cryptocurrency stolen from the 2022 LastPass breach. The analysis revealed...

EU renews UK data adequacy decisions until 2031
The European Commission's renewal of the UK's data adequacy decisions provides critical medium-term stability for transatlantic data flows, but the inclusion of a sunset...

Microsoft 365 Accounts Hijacked Through OAuth Device Code
Threat actors are weaponizing a legitimate Microsoft 365 feature to execute highly effective account takeovers that bypass multi-factor authentication. By abusing the OAuth 2.0...